VPC peering (console guide)
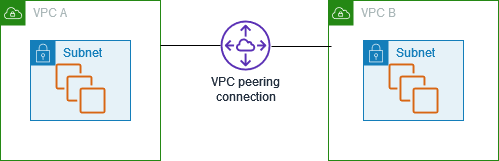
VPC peering connects two VPCs at Layer 3 with private IP routing. Use it for simple two-VPC or full mesh among few VPCs - not as a large-scale hub (use Transit Gateway instead).
Checklist: DevOps system design checklist
AWS diagram: VPC peering
Use cases
| Scenario | Fit |
|---|---|
| Shared services VPC (directory, tooling) | Peering to app VPCs |
| Acquisitions / two-team accounts (same region) | Peering + RAM optional |
| Database in VPC-A, app in VPC-B | Peering + SG referencing peer CIDR |
Poor fit: Many VPCs needing transitive access (A↔B and B↔C does not give A↔C through B).
Console steps
1. Create peering connection
- VPC console → Peering connections → Create peering connection.
- Requester VPC and Accepter VPC (same or cross-account).
- Cross-account: accepter must Accept in their account.
2. Enable DNS resolution (if needed)
- Select peering → Actions → Edit DNS settings.
- Enable Requester/accepter DNS resolution so private hosted zone names resolve across peer (requires associated zones).
3. Update route tables
Both sides need routes:
- Route tables → private RT for VPC-A → Edit routes → destination VPC-B CIDR → target pcx-xxxxx.
- Repeat in VPC-B for VPC-A CIDR.
Missing one side = asymmetric failures.
4. Security groups
SG rules can reference peer VPC CIDR or use referenced security group (same region peering).
IAM
Peering creation uses EC2 VPC IAM actions (ec2:CreateVpcPeeringConnection, ec2:AcceptVpcPeeringConnection). No special service role for data plane.
Security
- Peering is private - traffic does not traverse internet.
- Still apply least-privilege SG; peering is not a security boundary by itself.
- Network ACLs apply per subnet - verify both directions.
Commonly missed
| Item | Detail |
|---|---|
| Non-transitive | No “route through peer VPC” to a third VPC |
| Overlapping CIDRs | Peering rejected or routing broken |
| One-way routes | Works ping one direction only |
| DNS | Hostnames fail without DNS resolution option + PHZ association |
| NACL deny | Overrides SG allow |
Troubleshooting
| Symptom | Fix |
|---|---|
Peering pending-acceptance | Accept in accepter account |
active but no traffic | Routes on both RTs; SG/NACL |
| DNS NXDOMAIN cross-VPC | DNS resolution + private zone association |
| Need 10+ VPC mesh | Migrate design to TGW |
Docs: VPC peering